AI app builders have published thousands of apps that leak data
Platforms such as Lovable, Base44, Replit and Netlify let anyone build web apps without code in a matter of seconds. But a close analysis found that developers often forget to remove sensitive data, including API keys, passwords and client IDs, before publishing to the open web. Wired researchers found thousands of publicly accessible apps containing critical confidential data. Nobody is doing anything about it.
AI-processed from Wired; edited by Hamidun News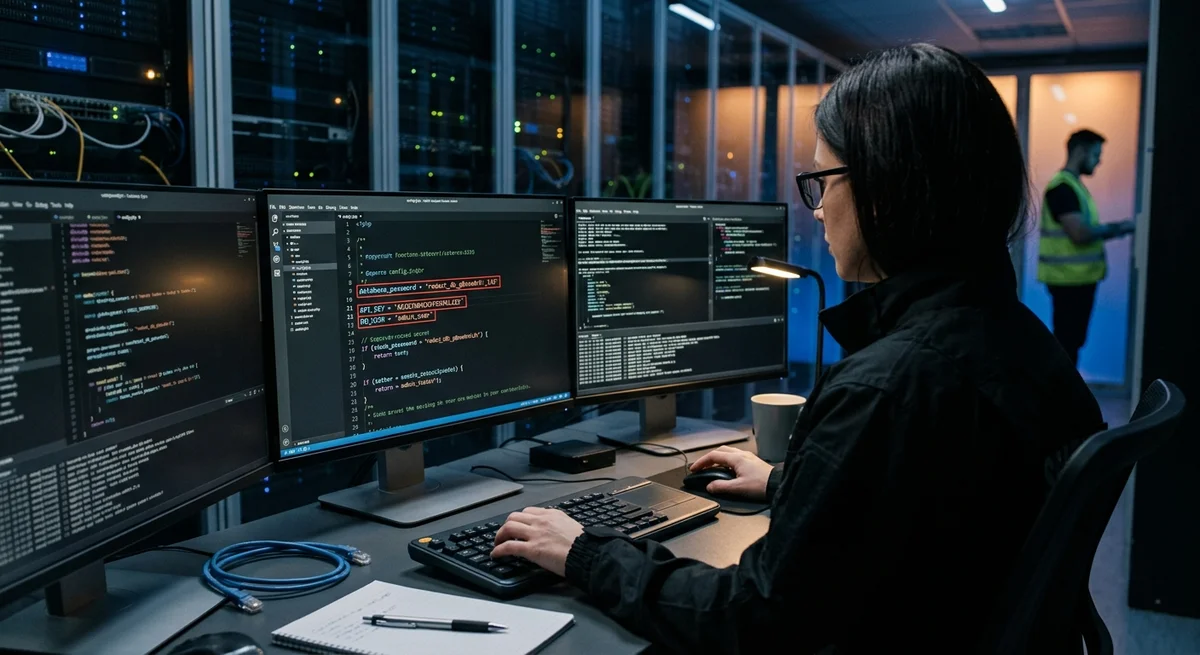
Platforms such as Lovable, Base44, Replit and Netlify use AI to let anyone, even people with no programming skills, build full-featured web apps in a matter of seconds. But Wired researchers have found a crack in this utopia: thousands of apps containing critical confidential data, including API keys, passwords and authorization tokens, sit openly on the internet. And nobody is doing anything about it.
How AI builders work
Services such as Lovable and Base44 are built on large language models like GPT-4. The developer simply describes what they need: "Build an expense-tracking app with Stripe integration." Within seconds, the system generates a complete React component or Vue app with a frontend and logic. The project can then be published right away through Netlify with a single button, or hosted on Replit.
This is revolutionary for development speed. An MVP usually takes weeks or months of work. Here it takes hours, sometimes minutes. It is no surprise that hundreds of thousands of developers have started using these services.
The scale of the problem
Wired set out to check what ends up in public view. The researchers analyzed thousands of apps built on these platforms and published to the open internet. The result was alarming: a significant share contained API keys, database passwords and other confidential data.
These are not isolated cases of carelessness. It is a systemic problem: the platforms have no mechanisms to prevent leaks. When code is generated automatically and published with one button, the security review process simply disappears.
What data is leaking
- Third-party API keys — OpenAI, Stripe, AWS, Google Cloud, Twilio. All of them sit in client-side JavaScript that anyone can download.
- Database passwords — credentials for MongoDB, PostgreSQL and MySQL are often not hashed and are visible as plain text in the app's source.
- Authorization tokens and session cookies — which can be used to hijack other people's accounts.
- Private encryption keys — used to protect user data.
- Internal IDs and architecture — even if harmless individually, together they reveal the app's structure to attackers.
When the researchers found these keys, they were able to access accounts and user data. What's more, bots that constantly scan the internet for such leaks are already finding them automatically.
Why this happens
The main reason is simple: development speed leaves no time for security. When an MVP can be built in 10 minutes, there is no code review, no vulnerability check and no standard process. On larger projects, this would be caught.
The second reason is that the platforms themselves do nothing. They do not warn the developer that an API key was found in the code. There is no automatic scrubbing of sensitive data. There is no prompt such as "Make sure you have removed all passwords before publishing." You just publish, and that's it.
The third reason is that developers are untrained. A person who could not code yesterday is building an app with real logic today. Nobody has explained basic security rules to them.
What this means
This is a classic case of democratization that has gone somewhat wrong. The tools do let more people build. But the room for error grows too.
For businesses: if you use these platforms for production apps, simply generating the code is not enough. Be sure to check it manually for leaks before publishing. Look for API keys in the source, passwords in configs and private data in logs.
For the platforms themselves, this is a critical moment. They need built-in security checks, warnings when keys are detected, and perhaps even a refusal to publish. Otherwise their reputation will suffer.
- Nov 2, 2026Arca gives AI agents finance tasks lasting up to 10 days, but leaves the trades to humans
- Nov 2, 2026Meta's Muse assistant keeps dossiers on loved ones and gets root on Ubuntu by default
- Nov 1, 2026Local models lose to Opus and Codex: 0.21 on a MacBook versus 1.00 for Codex
- Nov 1, 2026Kimi scores 96.2% on a 1C database analytics test and emerges as a fallback if Claude access is blocked
Key Questions Answered
How AI builders work?
Services such as Lovable and Base44 are built on large language models like GPT-4. The developer simply describes what they need: "Build an expense-tracking app with Stripe integration." Within seconds, the system generates a complete React component or Vue app with a frontend and logic. The project can then be published right away through Netlify with a single button, or hosted on Replit. This is revolutionary for development speed. An MVP usually takes weeks or months of work. Here it takes hours, sometimes minutes. It is no surprise that hundreds of thousands of develope
What are the key details on The scale of the problem?
Wired set out to check what ends up in public view. The researchers analyzed thousands of apps built on these platforms and published to the open internet. The result was alarming: a significant share contained API keys, database passwords and other confidential data. These are not isolated cases of carelessness. It is a systemic problem: the platforms have no mechanisms to prevent leaks. When code is generated automatically and published with one button, the security review process simply disappears.
What data is leaking?
Third-party API keys — OpenAI, Stripe, AWS, Google Cloud, Twilio. All of them sit in client-side JavaScript that anyone can download. Database passwords — credentials for MongoDB, PostgreSQL and MySQL are often not hashed and are visible as plain text in the app's source. Authorization tokens and session cookies — which can be used to hijack other people's accounts. Private encryption keys — used to protect user data. Internal IDs and architecture — even if harmless individually, together they reveal the app's structure to attackers. When the researchers found these keys, t
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.