Scammers distribute fake Claude installers with malware
Scammers copy Claude websites and release fake installers instead of the real application. Users think they are installing an AI assistant, but instead get malware. How to avoid it? Look for typos in the domain name, poor Russian translation, and links from spam or social media.
AI-processed from Habr AI; edited by Hamidun News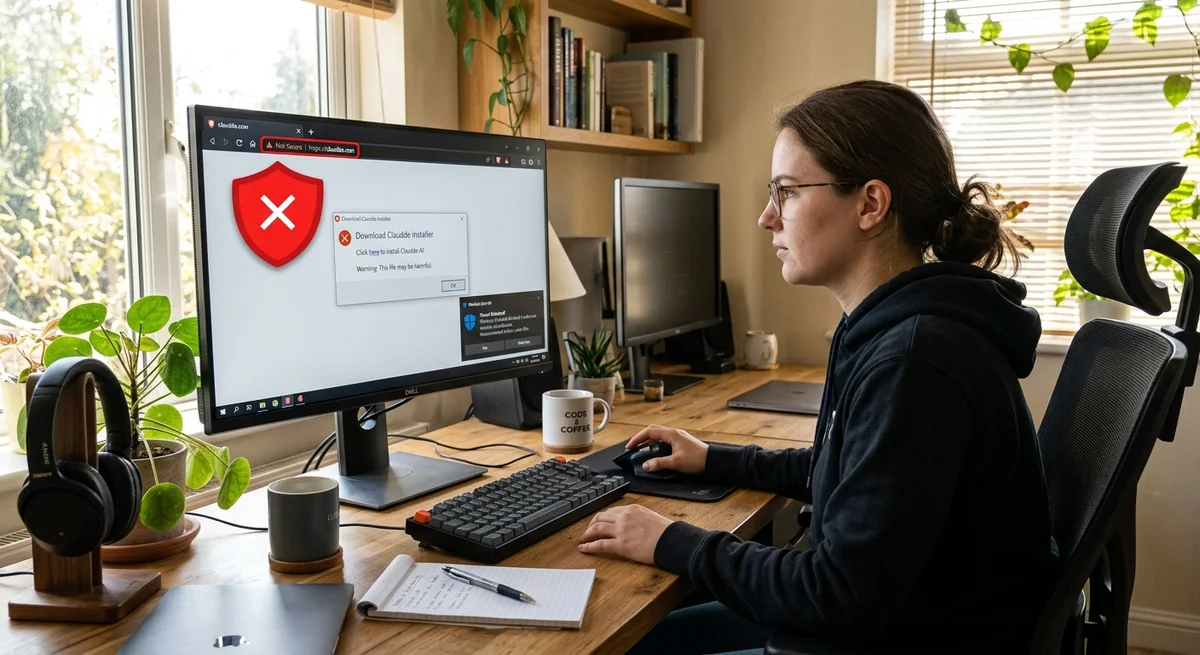
New trend on the dark side of the internet: scammers create fake websites for Claude, ChatGPT, and other popular AI tools, then distribute malicious "installers" through spam and social media. The inattentive user clicks a link, thinking they're downloading an interesting AI assistant — and gets malware.
How the Attack Works
The scheme is simple but effective. Scammers create websites that look almost identical to the original claude.com — same logos, colors, text. But the domain name differs by one or two letters: `claudde.com`, `claud3.com`, `claде.com` (with Cyrillic characters instead of Latin). Such typos are easy to miss if you're in a hurry. Links to fake sites are distributed through spam mailings, fake accounts on LinkedIn and Telegram, and search results via SEO manipulation. The victim clicks — and sees a beautifully designed download page with a "Download Installer" button. The file downloads, the user runs it — and instead of Claude, a trojan installs.
What's Inside the Fake Installer
The contents depend on the hacker's skill. In simple cases, it's an ordinary trojan that steals account credentials and saved passwords from the browser. In more complex cases — a modular malware that can download additional components: spyware, crypto-miner, ransomware. The cunning lies in disguise. While the malware runs in the background, the user sees a Claude installation window, waits a few minutes, gets a success message. Everything looks normal. But in the background, malicious processes are already running and hidden.
- Trojan for stealing passwords and cookies
- Spyware that logs keystrokes and screenshots
- Crypto-miner consuming your PC's electricity
- Backdoor for hackers' remote access
- Ransomware that encrypts files for ransom
How Not to Fall for It
The main rule — download AI tools ONLY from official sources. For Claude, that means: web application claude.ai (browser only, nothing to install), mobile app from App Store (iOS) or Google Play (Android), source code and API at github.com/anthropic-ai (for developers).
The second rule — don't be lazy about checking the link before clicking. Hover over the button, look at the bottom left corner of your browser — what URL is shown there? If it's not claude.ai and not anthropic.com — don't click.
The third rule — pay attention to details. Fake websites are often poorly made: typos in Russian translation, strange design, lack of HTTPS (no green lock next to the address in your browser). Official claude.ai always uses a secure connection.
What This Means
As AI tools grow in popularity, so do attacks on users. Scammers understand that people want to try Claude or ChatGPT, and they use this desire as a hook for distributing malware. That's why the main shield is vigilance and a simple rule: links from social media and emails are enemies, the official website is a friend.
- Oct 28, 2026A 2015 CNN Beat GPT-6 Astra and Claude Fable 5.1 at Skin Cancer Diagnosis
- Oct 28, 2026Keystone removes the model name from code: open-source LLM gateway adds 0.64 ms
- Oct 28, 2026Wired Tested 6 AI Agents in a Day: Dots Leads, Gemini Spark Fails at Lunch
- Oct 28, 2026Anthropic files for IPO: $16.3 billion in revenue in six months, ticker ANT
Key Questions Answered
How the Attack Works?
The scheme is simple but effective. Scammers create websites that look almost identical to the original claude.com — same logos, colors, text. But the domain name differs by one or two letters: `claudde.com`, `claud3.com`, `claде.com` (with Cyrillic characters instead of Latin). Such typos are easy to miss if you're in a hurry. Links to fake sites are distributed through spam mailings, fake accounts on LinkedIn and Telegram, and search results via SEO manipulation. The victim clicks — and sees a beautifully designed download page with a "Download Installer" button. The file
What's Inside the Fake Installer?
The contents depend on the hacker's skill. In simple cases, it's an ordinary trojan that steals account credentials and saved passwords from the browser. In more complex cases — a modular malware that can download additional components: spyware, crypto-miner, ransomware. The cunning lies in disguise. While the malware runs in the background, the user sees a Claude installation window, waits a few minutes, gets a success message. Everything looks normal. But in the background, malicious processes are already running and hidden. Trojan for stealing passwords and cookies Spywa
How Not to Fall for It?
The main rule — download AI tools ONLY from official sources. For Claude, that means: web application claude.ai (browser only, nothing to install), mobile app from App Store (iOS) or Google Play (Android), source code and API at github.com/anthropic-ai (for developers). The second rule — don't be lazy about checking the link before clicking. Hover over the button, look at the bottom left corner of your browser — what URL is shown there? If it's not claude.ai and not anthropic.com — don't click. The third rule — pay attention to details. Fake websites are often poorly made:
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.