Amazon Bedrock now tracks inference costs by user and application
AWS has added granular inference cost attribution to Amazon Bedrock. The platform now automatically ties costs to an IAM user, role or federated session, and tags let teams roll up spending by team, project and tenant. The feature is especially useful for companies running several applications, internal AI teams and LLM gateways, where all traffic could previously collapse into a single billing line.
AI-processed from AWS Machine Learning Blog; edited by Hamidun News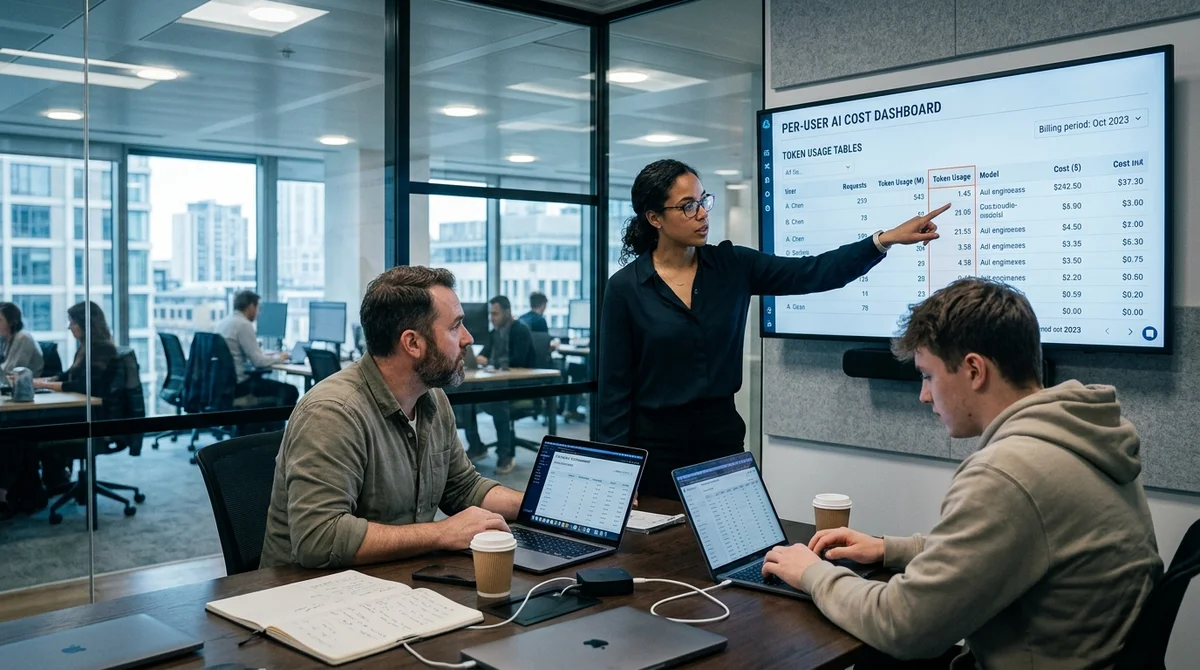
On April 17, 2026, AWS launched granular cost attribution for Amazon Bedrock, a detailed breakdown of inference spending. Costs can now be automatically tied to a specific user, application, IAM role or tenant, without changing how existing workloads call models.
How it works
Bedrock now passes AWS Billing data on which IAM principal sent each request to a model. That can be an ordinary IAM user, an application role, a temporary federated session through Okta or Entra ID, or a Bedrock API key if it is linked to an IAM identity.
The CUR 2.0 report gains a line_item_iam_principal field, and line_item_usage_type shows which model was used, in which region, and whether the money went to input or output tokens.
AWS also offers cost allocation tags on top of this. They can be attached directly to IAM users and roles, or passed as session tags during federated authorization and AssumeRole. Once activated in billing, these tags appear in both CUR 2.0 and Cost Explorer, where spending can be grouped by team, project, cost center or tenant.
The feature is available in commercial regions at no extra charge, but you must enable IAM principal export in CUR 2.0 and wait 24–48 hours for tags to appear.
"Understanding exactly who is spending money on inference is the first
step toward chargeback, forecasting and optimization."
Four accounting scenarios
AWS describes four typical setups where the new attribution is especially useful. The logic is the same: whoever calls Bedrock becomes the unit of accounting. But the tagging method depends on whether a person, a service, a corporate SSO session or a shared LLM gateway is working with the models.
The difference matters because it determines where the caller's identifier and tags are stored for later aggregation of costs in reports and alerts.
- IAM users and API keys suit small teams and prototypes: you can see each developer's spending separately.
- IAM roles for applications work well for production services: costs split by backend, batch job and project.
- Federated users via an IdP appear by session name and tags from SAML or OIDC.
- LLM gateway or proxy fits SaaS and internal AI platforms that need a breakdown by user and tenant rather than one shared line for the whole gateway.
The gateway is the trickiest case. If the proxy calls Bedrock under a single role, billing sees only that role and loses the detail. AWS suggests solving this with AssumeRole for each user or tenant, passing a role-session-name and tags. The resulting credentials can be cached for up to an hour, so the model does not require calling STS on every request. The default STS limit for AssumeRole is 500 calls per second per account, which matters for high-throughput systems.
What it means for teams
For FinOps and AI platform teams, this closes a long-standing gap: Bedrock costs were often visible only at the account level or for a single service user, and teams had to build their own logging layer and allocate costs manually. Now AWS provides a native chargeback and showback mechanism through the same IAM identities and tags companies already use for access and governance. Another plus: you can quickly see who is running expensive models such as Opus, who is on lighter configurations, and where output tokens are eating the budget.
For engineering teams, the value goes beyond finance. If each microservice has its own role and each employee has their own federated session, the same mechanism improves both security and transparency. In multi-tenant SaaS this is especially useful: you can compare the cost of serving customers, build internal pricing and set Cost Explorer alerts by tag.
In effect, AWS turns the identity behind a model call into a full financial label, one that supports reporting without a separate data pipeline.
What this means
Amazon Bedrock becomes noticeably more convenient for companies scaling GenAI beyond dozens of demo requests to real teams, services and customers. The more AI traffic a business has, the more it matters to see not just the total bill but the specific source of spending.
- Nov 2, 2026The Verge reviewer builds a $50 Meta Muse Charm alternative with Claude Code
- Oct 31, 2026Worldwide Express hands disputed invoices to AI agents and cuts unresolved disputes by 75%
- Oct 30, 2026AWS gives coding agents a live site preview straight from an isolated session
- Oct 30, 2026Agent traffic on Zocdoc is up 30x since July, and ChatGPT faces two health lawsuits
Key Questions Answered
How it works?
Bedrock now passes AWS Billing data on which IAM principal sent each request to a model. That can be an ordinary IAM user, an application role, a temporary federated session through Okta or Entra ID, or a Bedrock API key if it is linked to an IAM identity. The CUR 2.0 report gains a line_item_iam_principal field, and line_item_usage_type shows which model was used, in which region, and whether the money went to input or output tokens. AWS also offers cost allocation tags on top of this. They can be attached directly to IAM users and roles, or passed as session tags during f
What are the key details on Four accounting scenarios?
AWS describes four typical setups where the new attribution is especially useful. The logic is the same: whoever calls Bedrock becomes the unit of accounting. But the tagging method depends on whether a person, a service, a corporate SSO session or a shared LLM gateway is working with the models. The difference matters because it determines where the caller's identifier and tags are stored for later aggregation of costs in reports and alerts. IAM users and API keys suit small teams and prototypes: you can see each developer's spending separately. IAM roles for applications
What it means for teams?
For FinOps and AI platform teams, this closes a long-standing gap: Bedrock costs were often visible only at the account level or for a single service user, and teams had to build their own logging layer and allocate costs manually. Now AWS provides a native chargeback and showback mechanism through the same IAM identities and tags companies already use for access and governance. Another plus: you can quickly see who is running expensive models such as Opus, who is on lighter configurations, and where output tokens are eating the budget. For engineering teams, the value goes
Test Frontier LLMs & Autonomous Agents in One Workspace
Run Claude Opus 5.5, GPT-6, Gemini 3.1, and DeepSeek side-by-side in Nomad AI (nomadnet.ai) — unified model routing, deep research, and multimodal workflows under one subscription.
The AI world, distilled — once a week
Seven stories that actually mattered, hand-picked. No noise, no reposts, no press releases.
Done! Check your inbox for a confirmation.